

Cyber Security Consultancy London
Appropriate security for professional firms of 20 to 100 staff. The risks that matter, the basics done properly, and a senior consultant you can ask.
Most firms we meet have been managing security themselves, or through a general IT provider, and are not confident it is enough. We give you a clear view, a proportionate plan, and straight answers.
Cyber Essentials Plus certified
Microsoft partner since 2009

Britain’s Top 50 Best Managed IT Companies every year since 2018
Why firms come to us for cyber security advice
It is rarely because something has gone wrong. It is usually because someone has started asking questions and there is no confident answer.
Nobody owns it
Security has grown up alongside the IT, a bit at a time, and no one person can say what is in place or whether it is enough.
Someone is asking
A client questionnaire, a due diligence request, a cyber insurance renewal, the FCA, or a new board member. You need answers you can stand behind.
You are not sure the basics are in
Multi-factor authentication, leavers removed on the day, backups that have been tested, admin accounts under control. You think so, but you have not checked.
The advice does not fit
Every vendor has a product and every quote assumes you are a bank. You want someone to tell you what a firm your size needs, and what it does not.
Appropriate security, not a black hole
For a firm of 20 to 100 staff, cyber security has to be proportionate. Spend and attention go on the handful of risks that could stop the business or damage its reputation: identity and access, email, the data clients trust you with, backups, and the people who use all of it. Everything else is weighed against cost and disruption, not bought because it exists.
The threat has changed. Attackers now use AI to find weaknesses, write convincing phishing, and move through systems faster than a person could. That raises the floor: the basics have to be in place because gaps will be found. It does not mean a forty-person firm needs an enterprise security programme. It means the basics, done properly, checked, and explained.
Around half of UK businesses with 10 to 49 staff, and nearly two-thirds with 50 to 249, identified a breach or attack in the past year, and fewer than a third have assigned board-level responsibility for cyber security (Cyber Security Breaches Survey 2025/26). The gap is not technology. It is ownership and clarity.
How this works in practice
House Productions
Protecting intellectual property and satisfying investors and partners. We secured their Microsoft 365 and Box environments and took them through Cyber Essentials.
"Ratcliff IT have walked with us on our cyber security journey, helping us understand and identify the most important risks to satisfy our management team and our business partners. We're confident we're doing the right things to protect our critical intellectual property, assets, and reputation."
James Green, Finance Director, House Productions
The Ink Factory
Securing Microsoft 365, moving the team from Dropbox to Box for better control of data, and a security strategy backed by practical policies.
"The service is excellent and the attention to detail goes a long way. Thanks for the continued support!"
Sarah Ireland, Office Manager, The Ink Factory
What cyber security consultancy from Ratcliff IT looks like
Three things. An honest assessment, a plan that fits the business, and a senior person you can ask.
Cyber Security Assessment
A structured review of your Microsoft 365 or Google Workspace environment, identity and access, devices, email, backups, policies, and how your people work. You get a short, plain report: what is in place, what is not, what matters, and what to do first. Written for directors, not engineers.
A proportionate plan
The assessment becomes a prioritised roadmap, with costs, in the order the risks warrant. Where it helps, we align it to Cyber Essentials, Cyber Essentials Plus, or ISO 27001, and take you through certification. Where it does not, we say so.
Someone to ask
Questionnaires, insurance renewals, a supplier asking about your controls, a suspicious email, a leaver who had admin rights. A named senior consultant answers, and can present to your board when that is needed.
Day-to-day protection
Monitoring, patching, endpoint protection, and incident response are delivered as a managed service. See Cyber Security Services. Security awareness training for your team is part of that.
What we do not do
We do not host, secure, or manage web servers or public websites. If your website has been flagged for a vulnerability, or you need someone to look after the server it runs on, we will introduce you to people we trust and work alongside. Our focus is the business itself: your people, identities, devices, email, data, and the systems your firm runs on.
How it works
1
Discovery call
Thirty minutes with James or a senior consultant. What is worrying you, what has prompted it, and what is already in place. You get a view on whether an assessment is the right next step, and no pressure if it is not.
2
Assessment
We review the environment, the controls, and the way the firm works, and write it up in plain language with priorities and costs.
3
Plan and support
You act on the plan with us, with your existing IT provider, or on your own. Most clients keep us as the people they ask.
Consulting has been in the name since 2009
The company was registered as Ratcliff Consulting. The job has not changed: understand the business, ask whether there is a better way of doing things, and give a straight answer. You will work with senior people only, no juniors. We hold Cyber Essentials Plus ourselves, have been a Microsoft partner since 2009, and have been named one of Britain's Top 50 Best Managed IT Companies every year since 2018. We work with professional, well-run organisations in and around London, in asset management, property, life sciences, professional services, accountancy, and law.
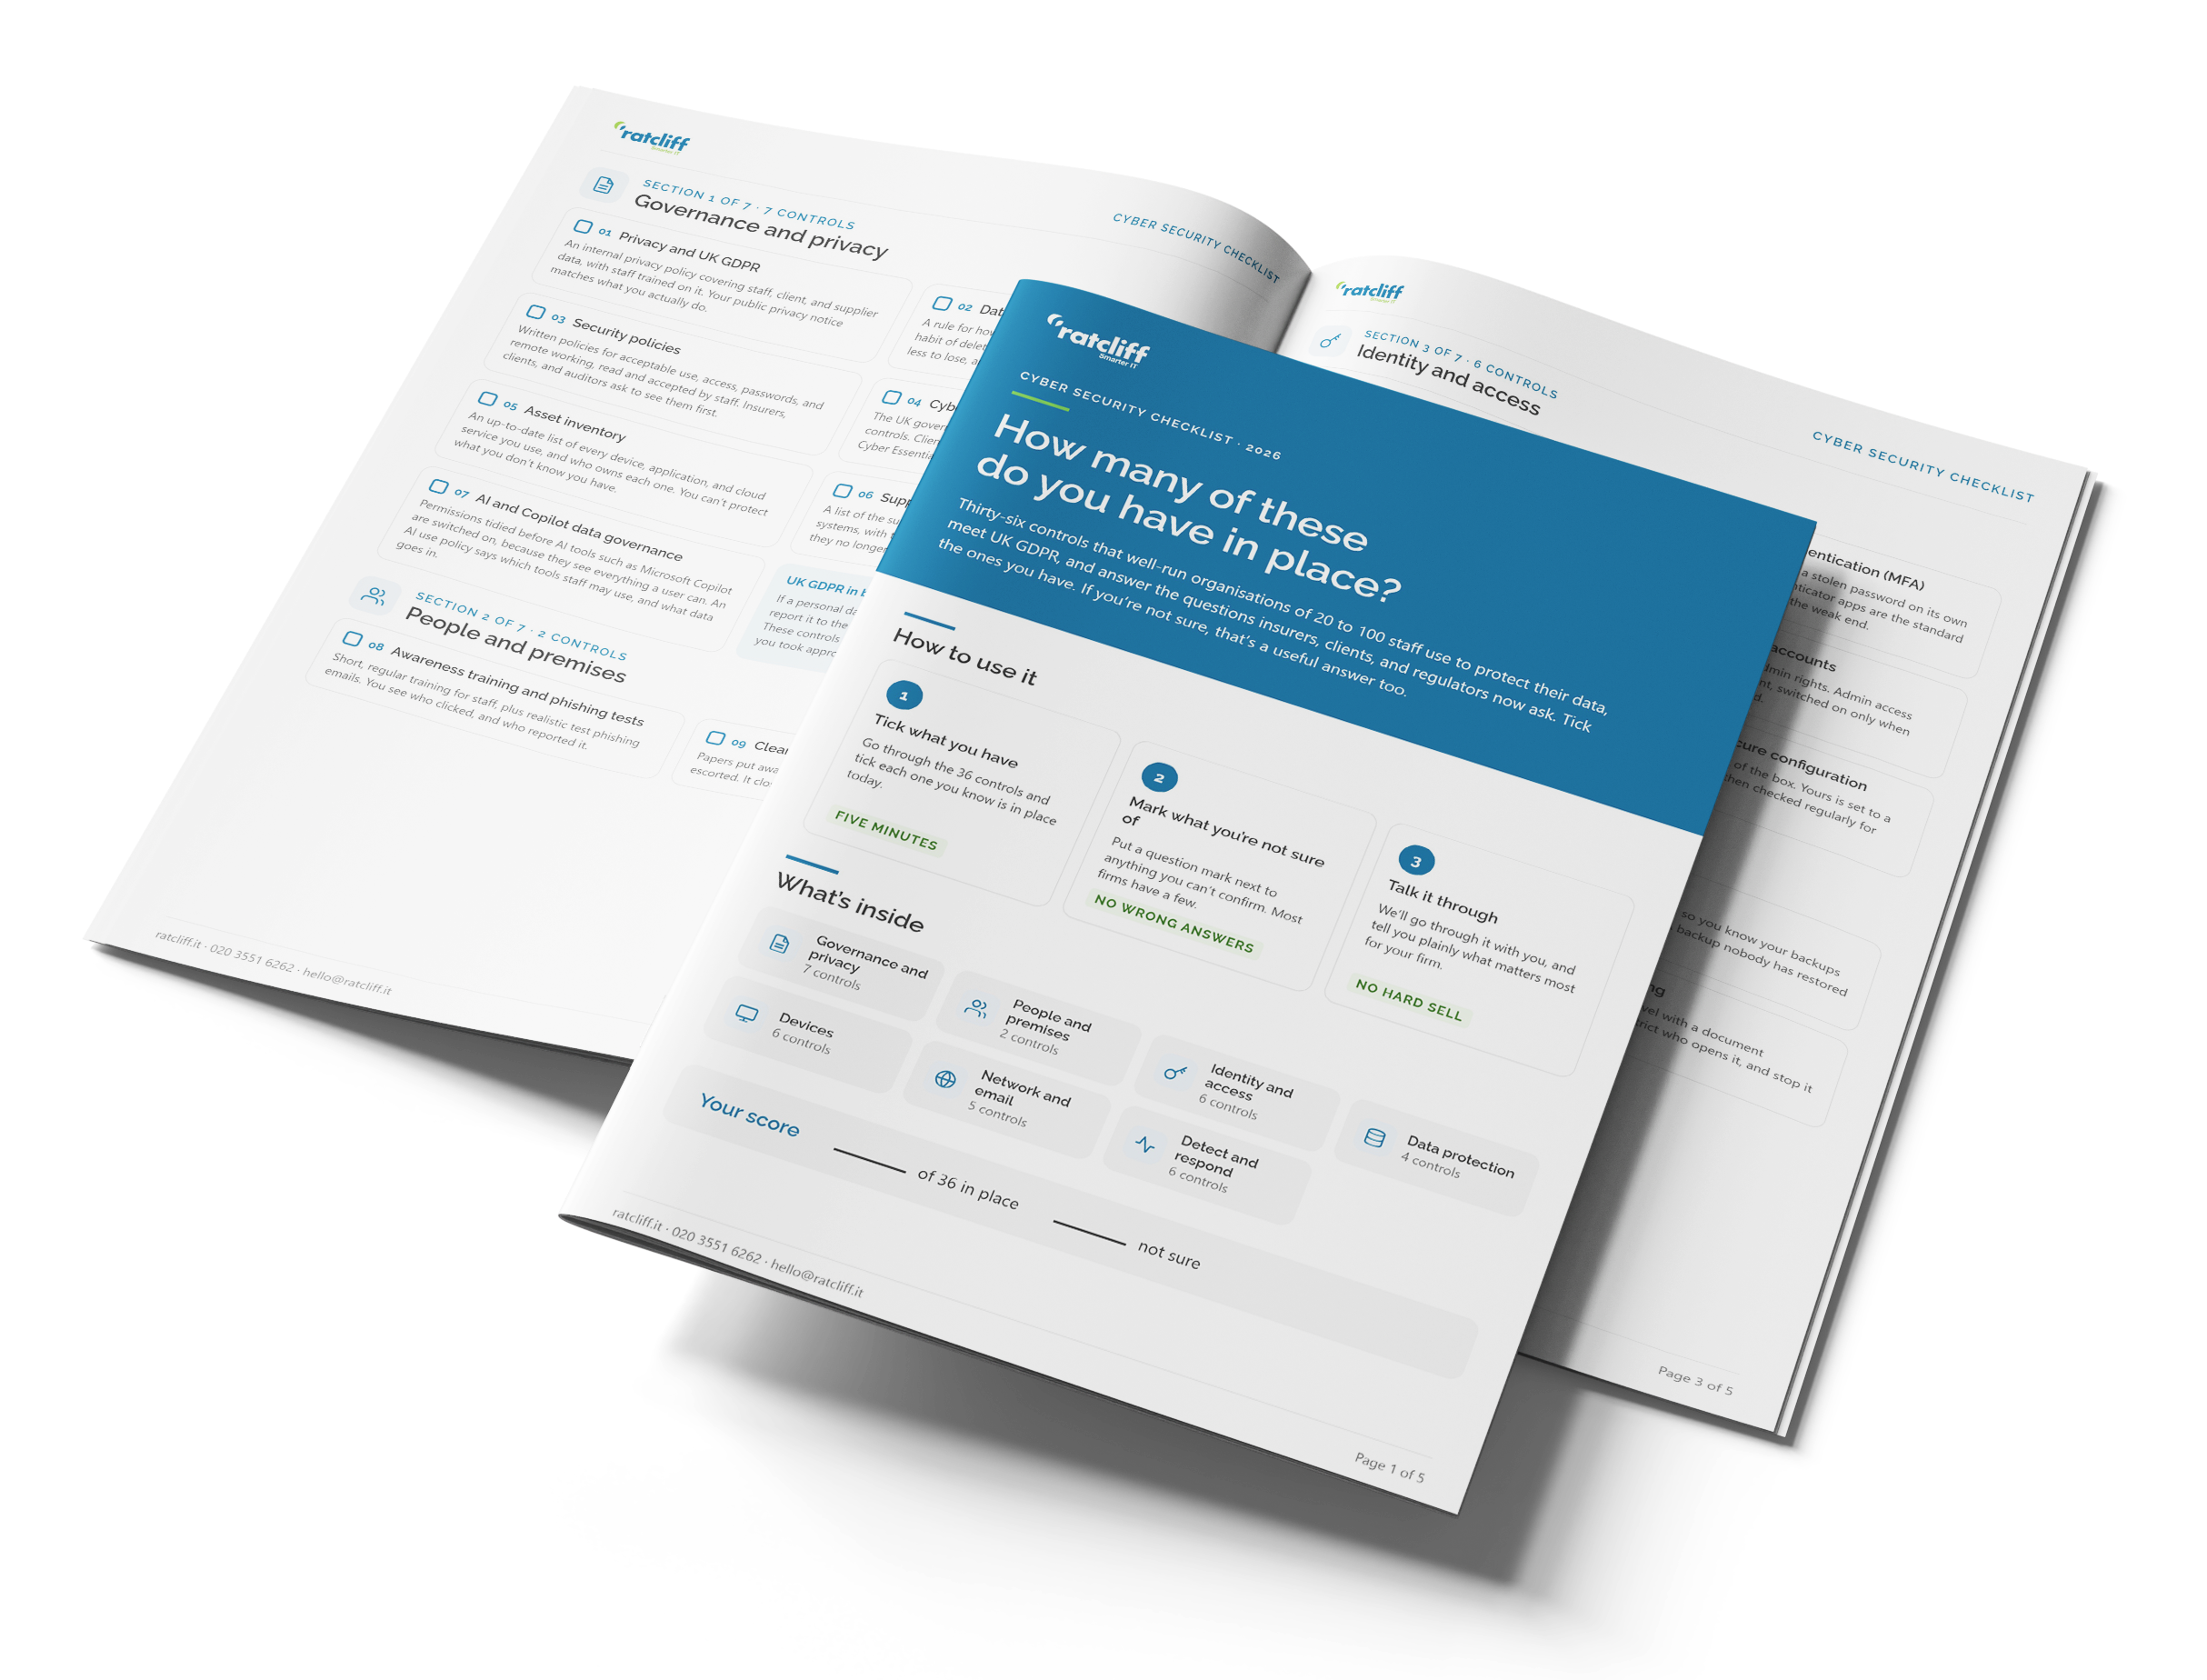
Download the cyber security checklist for firms of 20 to 100 staff
Based on what we find during onboarding, not generic advice. Microsoft 365 can be working and still be quietly insecure. The checklist covers the controls we review and enforce, including identity hardening, conditional access, and baseline configuration, aligned to Cyber Essentials and CIS.
Frequently asked questions
They work out what you need and what you do not. That means assessing what is in place, identifying the risks that could stop the business or damage its reputation, and setting out a proportionate plan with costs. They are also the person you ask when a client, insurer, or regulator wants answers.
Less than most vendors will tell you and more than most firms have. The basics, done properly, cover most of the risk: multi-factor authentication everywhere, admin accounts under control, leavers removed on the day, tested backups, protected devices, and staff who know what a phishing email looks like. Beyond that, it depends on your sector, your clients, and the data you hold.
No. A penetration test tries to break in and tells you where it got through. An assessment reviews how the firm is set up and run, from identity and access to backups and policies, and tells you what matters and what to do first. Most firms of this size need the assessment first. We arrange penetration testing through trusted partners where it is warranted.
Yes. This is one of the most common reasons firms come to us. We help you answer accurately, and where the honest answer is "no", we help you fix it.
Cyber Essentials is a sensible baseline for almost any firm, and many clients and insurers now expect it. Cyber Essentials Plus adds independent testing. ISO 27001 is a full management system and is worth it when clients or regulators require it. We will tell you which, if any, fits your firm, and take you through it.
Yes. We regularly assess environments run by other providers and work alongside them on the plan. We will be straight with you about what we find.
No. We do not host, secure, or manage web servers or public websites. If that is the need, we will introduce you to people we trust. Our work covers your people, identities, devices, email, data, and the systems your firm runs on.
Start with a conversation
If you are not confident your security is right for your firm, a discovery call is the quickest way to find out. Thirty minutes, no preparation needed, and a straight view on what to do next.
hello@ratcliff.it · 020 3551 6262 · 314 Regents Park Road, London N3 2JX
Cyber security insights
Webinar: Cyber Essentials: What every business needs to know
Read more →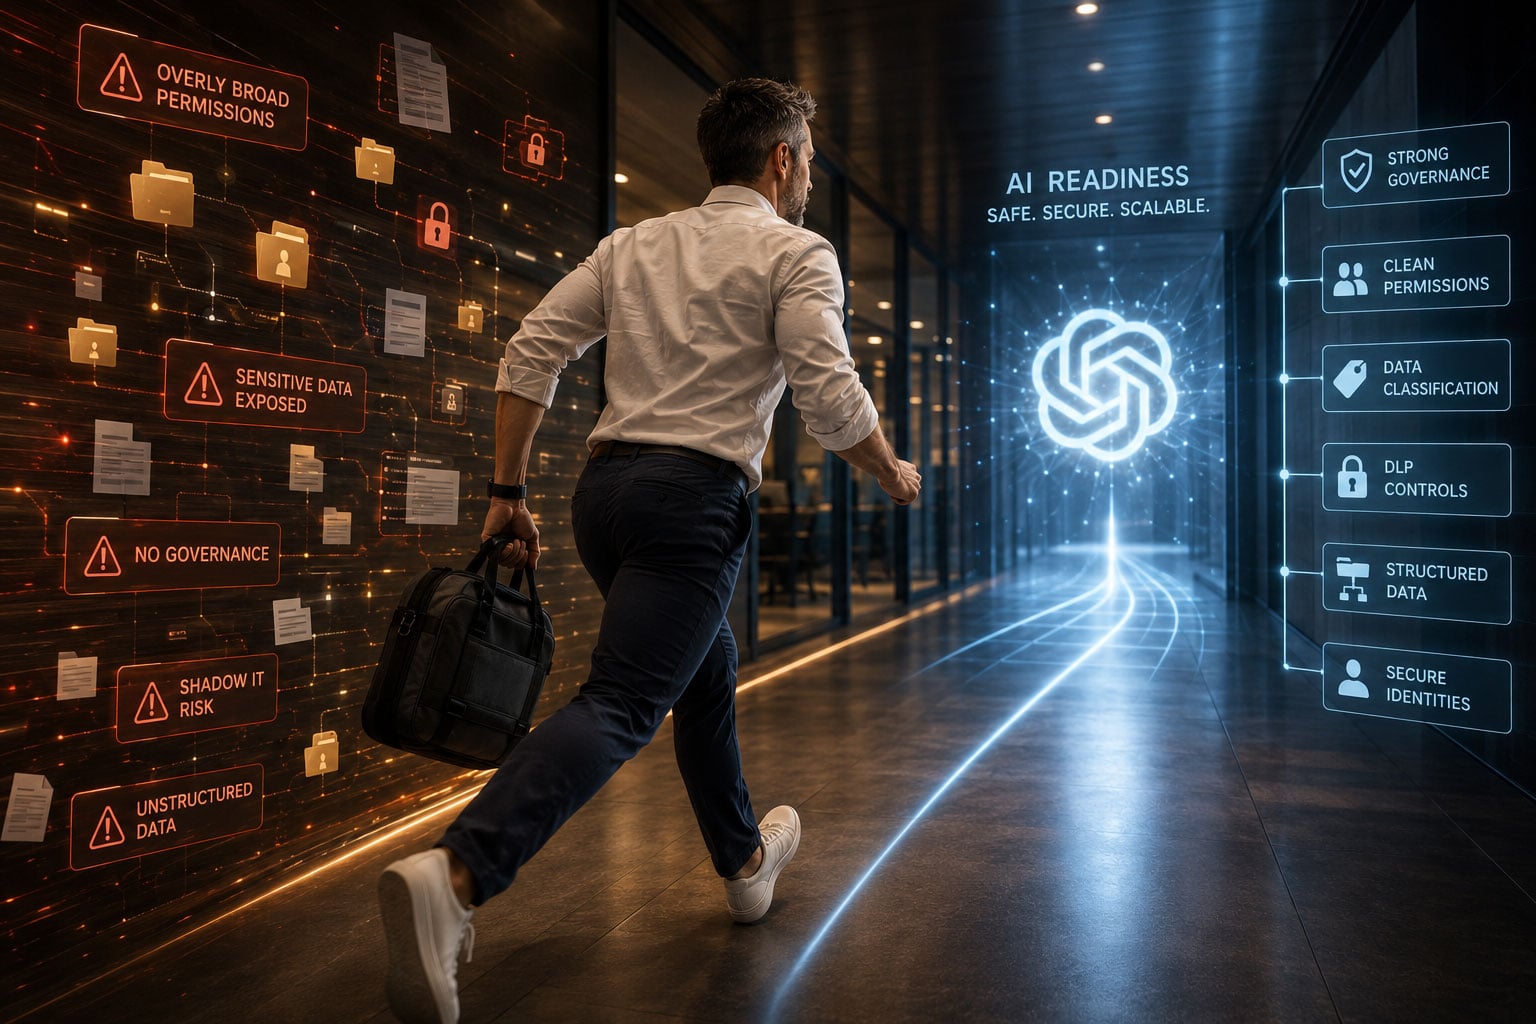
AI Readiness - Stop and Get your house in order
Read more →